On this page
Endpoint security for Linux is about protecting Linux systems from unauthorized access, malware, vulnerable software, misconfiguration, and other security threats. Linux endpoint security combines several layers of protection, including secure remote access, firewall rules, software updates, file permissions, malware detection, and system monitoring.
Linux has a strong security foundation, but a secure operating system does not automatically mean a secure server. Poor SSH settings, unnecessary services, outdated packages, and exposed ports can still create serious risks.
This guide explains how to improve endpoint security for Linux with practical steps that can be applied to a VPS, dedicated server, or Linux hosting environment.
What Is Linux Endpoint Security?
Linux endpoint security is the process of protecting Linux devices and servers against threats that could compromise the operating system, applications, data, or user accounts.
An endpoint can be a desktop computer, workstation, virtual machine, or server. In hosting environments, Linux servers are particularly important because one compromised server can affect websites, databases, email services, and other applications running on it.
Linux endpoint security usually involves several layers:
| Security layer | What it protects |
|---|---|
| SSH security | Remote server access |
| Firewall | Network connections and exposed ports |
| Software updates | Known vulnerabilities in packages |
| File permissions | Files, directories, and sensitive data |
| Malware detection | Malicious files and processes |
| Logging | Suspicious activity and security events |
| User accounts | Unauthorized or excessive access |
| Backups | Recovery after compromise or data loss |
The goal is not to rely on one security tool. Effective Linux endpoint security comes from combining several controls and regularly checking that they are working.
Why Is Linux Endpoint Security Important for Servers?
A Linux server can remain online for months or years and may be reachable from the public internet the entire time. That makes server security different from securing a personal computer.
An attacker does not necessarily need to break through a sophisticated vulnerability. A weak password, exposed service, outdated package, or incorrectly configured permission can sometimes provide the initial entry point.
Once an attacker gains access, they may attempt to:
- Create unauthorized accounts
- Install malware
- Steal credentials
- Modify website files
- Access databases
- Run unwanted processes
- Use the server for spam or attacks
- Move deeper into the system
- Delete or encrypt important data
Good endpoint security reduces the number of ways an attacker can enter the system and limits what they can do if something goes wrong. This broader process of reducing the attack surface is commonly referred to as Linux hardening.
What Are the Main Linux Endpoint Security Risks?
Before adding security tools, understand what you are actually protecting against.
Weak SSH credentials
SSH is one of the most common ways administrators access Linux servers. Weak passwords and poorly protected accounts can make remote access an easy target.
Using SSH keys, limiting administrative access, and disabling unnecessary authentication methods can significantly improve security.
Unnecessary open ports
Every publicly accessible service increases the server’s attack surface.
A web server may need ports for HTTP and HTTPS, while SSH requires its own access port. Other services should not be exposed publicly unless there is a clear reason for doing so.
Outdated software
Security vulnerabilities are regularly discovered in operating systems, libraries, applications, and server software.
Keeping packages updated helps close known security weaknesses before they can be exploited.
Incorrect file permissions
Linux permissions control who can read, write, or execute files. Poor permissions can allow one compromised application or user to access data belonging to another.
Malicious processes and files
A compromised server may contain suspicious scripts, unauthorized binaries, modified system files, or processes that consume unusual amounts of CPU or memory.
Poor monitoring
A server can be compromised without immediately showing obvious symptoms. Logs and system monitoring provide valuable evidence when investigating unusual activity.
How to Secure SSH Access on Linux
SSH provides encrypted remote access to Linux systems, but it should be configured carefully.
Start by connecting with a specific user instead of unnecessarily using the root account for everyday administration:
ssh username@server-ipSSH keys are generally preferable to relying only on passwords.
You can create an Ed25519 key pair with:
ssh-keygen -t ed25519After installing the public key on the server, test the connection before changing password authentication.
You should also review your SSH configuration and avoid making changes without first confirming that your current access method works. Locking yourself out of a remote server is an easy mistake to make.
Other useful SSH security measures include:
- Use strong authentication
- Prefer SSH keys where appropriate
- Restrict SSH access to trusted networks when possible
- Disable unnecessary users
- Review failed login attempts
- Keep OpenSSH updated
- Avoid exposing additional administrative services unnecessarily
If you want to understand SSH authentication, key pairs, ports, and secure remote access in more detail, see our guide to SSH Secure Shell.
How to Use a Firewall for Linux Endpoint Security
A firewall controls network traffic entering or leaving the server. It can prevent unwanted connections from reaching services that should not be publicly accessible.
Before changing firewall rules, identify the services that actually need external access.
For example, a typical web server may need:
HTTP   80
HTTPS  443
SSH 22The exact ports depend on your configuration.
Do not simply open a large range of ports because an application might need them. Determine which services are running and expose only what is required.
If you use CSF, our guide on how to configure the CSF firewall can help you review firewall rules and allowed ports.
A firewall is not a replacement for secure applications or authentication. It is another layer that reduces unnecessary exposure.
How to Keep Linux Packages and Software Updated
Updates are one of the simplest parts of server security to overlook.
Start by checking available updates using your distribution’s package manager.
On Debian or Ubuntu:
sudo apt update
sudo apt upgradeOn systems using DNF:
sudo dnf check-update
sudo dnf upgradeThe exact commands depend on the Linux distribution and version.
Updates should be tested appropriately on production systems, especially when they involve important applications or services. At the same time, delaying security updates indefinitely leaves known vulnerabilities available for longer than necessary.
A good approach is to maintain a regular update process and pay particular attention to security advisories affecting software exposed to the internet.
How to Protect Linux Files and Directories
File permissions are an important part of endpoint security for Linux.
Linux permissions determine whether users and groups can read, write, or execute a file.
You can inspect permissions with:
ls -laFor example:
-rw-r--r-- 1 user user 1024 example.txtThe permission string tells you who can access the file and what they can do with it.
Avoid giving files or directories broader permissions than necessary. Commands such as this should not be used as a generic solution:
chmod -R 777 /some/directoryAlthough it may appear to fix permission errors, it can also make sensitive files writable by users who should not have that access.
Instead, identify the application and user that need access and assign the minimum permissions required.
This principle is especially important on hosting servers where multiple websites and services may share the same machine.
How Can Malware Detection Improve Linux Endpoint Security?
Malware detection adds another layer to Linux endpoint security, particularly on servers that host websites, applications, or user-uploaded files.
Start with basic system inspection. You can view running processes with:
ps auxYou can also check resource usage with:
topor:
htopLook for processes you do not recognize, unexpected resource consumption, unusual users, or applications running from suspicious locations.
For organizations managing many Linux endpoints, commercial security platforms can also provide centralized monitoring and threat detection. For example, Bitdefender endpoint security tools for Linux can be considered when an environment requires dedicated endpoint protection beyond basic operating system controls.
The right security tool depends on the environment, the type of workloads being hosted, compliance requirements, and the level of centralized management required.
However, do not assume that installing an endpoint security product makes the server secure by itself. It should complement secure authentication, patching, firewall rules, permissions, monitoring, and backups.
How to Monitor Linux Logs for Security Issues
Logs can provide some of the earliest clues that something unusual is happening.
Depending on the distribution and services installed, useful information may be available through system logs, authentication logs, web server logs, and application logs.
For systems using systemd, you can inspect journal entries with:
sudo journalctlTo review recent entries:
sudo journalctl -n 100For SSH-related activity, authentication logs can be particularly useful.
Look for patterns such as:
- Repeated failed login attempts
- Successful logins from unexpected locations
- Unknown users
- Unexpected service restarts
- Repeated application errors
- Unusual privilege escalation activity
Do not let logs grow without a management strategy. Proper Linux log rotation helps keep log files under control while preserving useful historical information.
How Does CyberPanel Help With Linux Server Security?
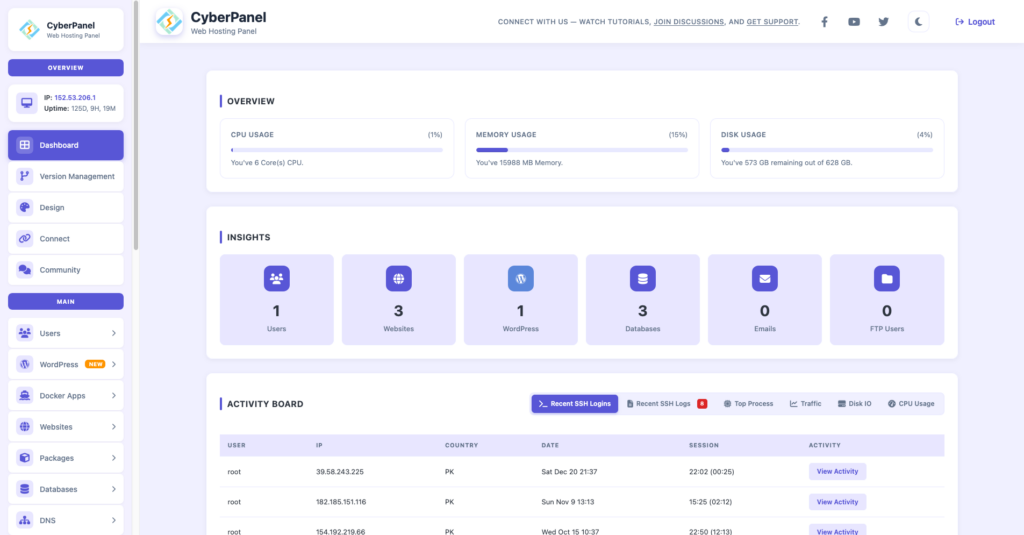
CyberPanel is a free and open-source web hosting control panel. It does not replace Linux security controls. Instead, it provides a management layer for a Linux hosting server, allowing administrators to manage websites, services, domains, databases, and other hosting functions through a web interface.
The underlying server still needs proper security configuration.
For a CyberPanel server, endpoint security can include:
- Securing SSH access
- Configuring firewall rules
- Keeping the operating system and software updated
- Using appropriate file and directory permissions
- Monitoring server and application logs
- Removing unnecessary services
- Protecting websites and databases
- Maintaining reliable backups
- Monitoring unusual server activity
This distinction matters because a control panel can simplify administration, but it cannot eliminate the need for operating system security.
For example, if SSH is exposed to the internet, it still needs to be secured even when the server is managed through CyberPanel.
How to Build a Linux Endpoint Security Checklist
Security is easier to maintain when it becomes a routine rather than a one-time configuration. If you are securing a new VPS, our VPS security checklist can help you review the main server hardening steps before putting the system into production.
| Area | Security check |
|---|---|
| SSH | Use strong authentication and review access |
| Firewall | Allow only required ports |
| Updates | Apply relevant security updates |
| Users | Remove unnecessary accounts and privileges |
| Permissions | Use least privilege file access |
| Services | Disable services that are not required |
| Logs | Monitor authentication and system activity |
| Malware | Investigate suspicious files and processes |
| Backups | Maintain tested and reliable backups |
| Monitoring | Watch for unusual resource or network activity |
The checklist should also change as the server changes. Installing a new application, opening a new port, adding a user, or changing permissions can introduce a new security risk.
Common Linux Security Mistakes to Avoid
Opening unnecessary ports
If a service does not need to be publicly accessible, there is usually little reason to expose it.
Using weak passwords
Administrative accounts are valuable targets. Use strong authentication and avoid sharing credentials between users.
Giving everything root access
Root access should be limited because a compromised privileged account can cause much more damage.
Using 777 permissions as a quick fix
Broad permissions can create security problems. Fix ownership and permissions according to the actual application requirements instead.
Ignoring logs
Logs are useful during both routine monitoring and incident investigation.
Installing security software without monitoring it
A security tool is only useful if it is configured correctly, maintained, and actually checked when it reports a problem.
Treating a firewall as complete security
A firewall can reduce network exposure, but it cannot fix vulnerable software, stolen credentials, insecure applications, or bad file permissions.
Linux Endpoint Security Best Practices
A practical Linux endpoint security strategy should follow a layered approach.
Start with the basics:
- Remove unnecessary services and accounts.
- Secure SSH and administrative access.
- Configure a firewall around actual service requirements.
- Keep the operating system and applications updated.
- Apply least privilege permissions.
- Monitor authentication and system logs.
- Investigate unexpected processes and network activity.
- Maintain reliable backups.
- Review the server after major configuration changes.
- Test your security controls instead of assuming they work.
Security is not a single configuration file or software package. It is an ongoing process of reducing exposure, monitoring the system, and responding when something changes.
FAQs
Is Linux secure enough without endpoint security?
No. Linux has strong security features, but administrators still need to configure and maintain them properly. Internet-facing servers require additional protection against unauthorized access, vulnerable software, malicious activity, and configuration mistakes.
What is the most important part of Linux endpoint security?
There is no single control that provides complete protection. Secure authentication, firewall configuration, timely updates, correct permissions, monitoring, and backups all contribute to a stronger security posture.
Is SSH safe for Linux servers?
SSH is designed for secure remote administration, but its security still depends on configuration and authentication. Strong credentials, SSH keys, restricted access, updates, and appropriate firewall rules can reduce the risk of unauthorized access.
Final Thoughts
Endpoint security for Linux works best as a layered process. Secure SSH access, limit exposed ports, keep software updated, control file permissions, monitor logs, and investigate anything that does not look right.
For CyberPanel users, the same principle applies. CyberPanel makes hosting management easier, but the underlying Linux server still needs proper security practices.
The strongest approach is simple: reduce unnecessary exposure, use the least privilege required, keep systems maintained, and monitor what is happening on the server.