On this page
Update checked at 13:39 UTC on 21 October 2026: upstream fixes released; applicable LiteSpeed packages still pending in our QA repository. CyberPanel QA and verified remediation are not complete.
PHP has released 8.2.35, 8.3.36, 8.4.27 and 8.5.12 for CVE-2026-109618 and CVE-2026-109619. Its advisory includes web-facing LiteSpeed installations. Updating to a fixed release, or an explicitly verified vendor backport, is required; configuration measures are not a complete fix.
Our fresh Ubuntu 26.04 QA repository check still returned 8.2.34, 8.3.35, 8.4.26 and 8.5.11. This finding applies to the repository we checked, not every operating system. We are monitoring for applicable packages and will test both website PHP and the separate panel PHP copy before publishing verified upgrade instructions.
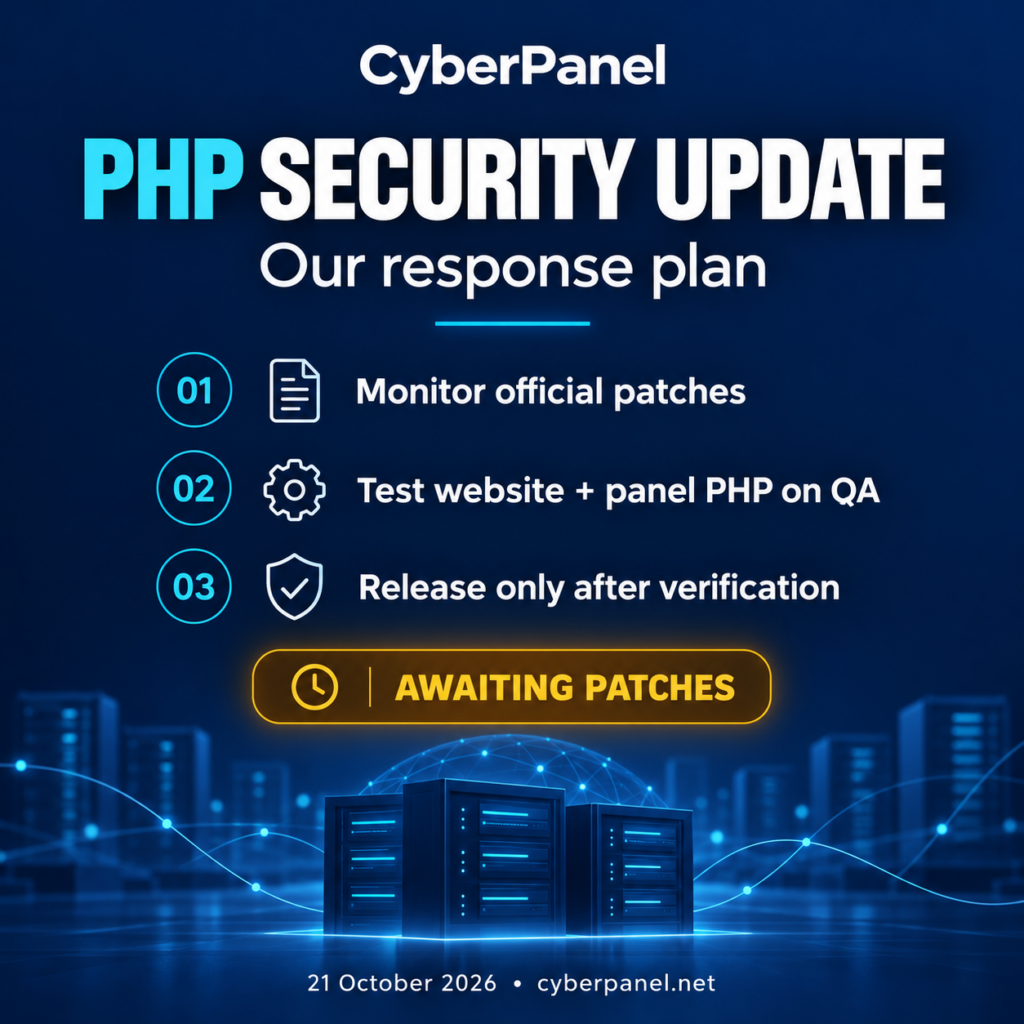
Read the official PHP security advisory, including its carefully qualified interim measures. PHP 8.1 and older require an evidenced vendor backport or migration to a supported release. Earlier announcement graphics reflect the initial monitoring stage.
Initial response plan — 21 October 2026, 09:10 UTC
Status at 09:10 UTC on 21 October 2026: monitoring and preparing; no verified fix announced yet.
We are tracking reports of PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. PHP’s official advance notice announces two critical vulnerabilities rated CVSS v4.0 9.2 and schedules its security release for 21 October at 14:00 UTC (7 PM Pakistan time). The notice says technical details, affected versions and fixed versions will accompany the release, which may be brought forward.
We have checked our owned CyberPanel QA environment and refreshed its LiteSpeed package repository. At our initial check, the installed PHP branches and available candidates were 8.2.34, 8.3.35, 8.4.26 and 8.5.11. This is evidence from that QA environment, not an inventory of every customer server or operating system. We have not established the exploitability of a particular customer deployment.
How we will handle the patches
- Check every 30 minutes. Track PHP’s official release and the applicable vendor packages. Confirm affected versions and package provenance before treating an update as a fix.
- Test on our owned QA server. Validate the applicable website PHP runtimes and CyberPanel’s separate panel PHP executable. Check the running HTTP version, phpMyAdmin, normal website operation and relevant regression tests, with backups and rollback available.
- Release verified remediation. After testing passes, publish any required CyberPanel changes and exact upgrade instructions. Confirm package versions and the running processes, including the panel PHP copy. A successful package installation or a CyberPanel version number alone does not prove the system is patched.
- Publish clear results. Update this post and our channels with what is fixed, what was tested, and any remaining operating-system or vendor-package limitations.
What administrators can do now
Identify the PHP versions used by each site and panel service, confirm backups and prepare a maintenance window. Follow official PHP and package-vendor guidance. Avoid treating unverified scripts, leaked exploit claims or guessed configuration changes as a complete fix. If a runtime is outside upstream security support, check for an explicitly supported vendor backport or plan migration to a supported branch.
The upstream release time is not a promise that every distribution’s binary packages will be ready at that moment. We will distinguish patch availability, completed QA and a verified release in each update.
Official sources: PHP advance notice and CERT-EU advisory.